

 Java EE












spring security 配置看不明,求助!!!
 墨衍会员 · AI 创作全网分发 墨衍智能分发 通过墨衍一键同步至各平台 可同步平台 CSDN微信公众号微博知乎掘金百家号博客园抖音小红书 你的文章也可以这样分发 墨衍会员 ¥399起/年,写一次发全网
我也要 关注 + 加入社区
security.xml配置文件如下:
<?xml version="1.0" encoding="UTF-8"?>
<beans:beans xmlns="http://www.springframework.org/schema/security" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
xmlns:beans="http://www.springframework.org/schema/beans"
xsi:schemaLocation="http://www.springframework.org/schema/beans http://www.springframework.org/schema/beans/spring-beans-2.0.xsd
http://www.springframework.org/schema/security http://www.springframework.org/schema/security/spring-security-2.0.1.xsd">
<http auto-config="true" lowercase-comparisons="false">
<!--intercept-url pattern="/images/*" filters="none"/>
<intercept-url pattern="/styles/*" filters="none"/>
<intercept-url pattern="/scripts/*" filters="none"/-->
<intercept-url pattern="/admin/*" access="ROLE_ADMIN"/>
<intercept-url pattern="/passwordHint.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/signup.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/a4j.res/*.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/bank*.html*" access="ROLE_ADMIN,ROLE_MANAGER"/>
<intercept-url pattern="/charge*.html*" access="ROLE_ADMIN,ROLE_MANAGER"/>
<!-- APF-737, OK to remove line below if you're not using JSF -->
<intercept-url pattern="/**/*.html*" access="ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<form-login login-page="/login.jsp" authentication-failure-url="/login.jsp?error=true" login-processing-url="/j_security_check"/>
<remember-me user-service-ref="userDao" key="e37f4b31-0c45-11dd-bd0b-0800200c9a66"/>
</http>
<!--关键是这里看不明,spring是将form里的j_username和j_password传递给userDao吗???-->
<authentication-provider user-service-ref="userDao">
<password-encoder ref="passwordEncoder"/>
</authentication-provider>
<!-- Override the default password-encoder (SHA) by uncommenting the following and changing the class -->
<!-- <bean id="passwordEncoder" class="org.springframework.security.providers.encoding.ShaPasswordEncoder"/> -->
<global-method-security>
<protect-pointcut expression="execution(* *..service.UserManager.getUsers(..))" access="ROLE_ADMIN"/>
<protect-pointcut expression="execution(* *..service.UserManager.removeUser(..))" access="ROLE_ADMIN"/>
</global-method-security>
</beans:beans>
###########################################################################################################
<!--关键是这里看不明,spring是将form里的j_username和j_password传递给userDao吗???-->
<authentication-provider user-service-ref="userDao">
<password-encoder ref="passwordEncoder"/>
</authentication-provider>
<?xml version="1.0" encoding="UTF-8"?>
<beans:beans xmlns="http://www.springframework.org/schema/security" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
xmlns:beans="http://www.springframework.org/schema/beans"
xsi:schemaLocation="http://www.springframework.org/schema/beans http://www.springframework.org/schema/beans/spring-beans-2.0.xsd
http://www.springframework.org/schema/security http://www.springframework.org/schema/security/spring-security-2.0.1.xsd">
<http auto-config="true" lowercase-comparisons="false">
<!--intercept-url pattern="/images/*" filters="none"/>
<intercept-url pattern="/styles/*" filters="none"/>
<intercept-url pattern="/scripts/*" filters="none"/-->
<intercept-url pattern="/admin/*" access="ROLE_ADMIN"/>
<intercept-url pattern="/passwordHint.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/signup.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/a4j.res/*.html*" access="ROLE_ANONYMOUS,ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<intercept-url pattern="/bank*.html*" access="ROLE_ADMIN,ROLE_MANAGER"/>
<intercept-url pattern="/charge*.html*" access="ROLE_ADMIN,ROLE_MANAGER"/>
<!-- APF-737, OK to remove line below if you're not using JSF -->
<intercept-url pattern="/**/*.html*" access="ROLE_ADMIN,ROLE_USER,ROLE_MANAGER"/>
<form-login login-page="/login.jsp" authentication-failure-url="/login.jsp?error=true" login-processing-url="/j_security_check"/>
<remember-me user-service-ref="userDao" key="e37f4b31-0c45-11dd-bd0b-0800200c9a66"/>
</http>
<!--关键是这里看不明,spring是将form里的j_username和j_password传递给userDao吗???-->
<authentication-provider user-service-ref="userDao">
<password-encoder ref="passwordEncoder"/>
</authentication-provider>
<!-- Override the default password-encoder (SHA) by uncommenting the following and changing the class -->
<!-- <bean id="passwordEncoder" class="org.springframework.security.providers.encoding.ShaPasswordEncoder"/> -->
<global-method-security>
<protect-pointcut expression="execution(* *..service.UserManager.getUsers(..))" access="ROLE_ADMIN"/>
<protect-pointcut expression="execution(* *..service.UserManager.removeUser(..))" access="ROLE_ADMIN"/>
</global-method-security>
</beans:beans>
###########################################################################################################
<!--关键是这里看不明,spring是将form里的j_username和j_password传递给userDao吗???-->
<authentication-provider user-service-ref="userDao">
<password-encoder ref="passwordEncoder"/>
</authentication-provider>
...全文
相关推荐
详解spring security 配置多个AuthenticationProvider
主要介绍了详解spring security 配置多个AuthenticationProvider ,小编觉得挺不错的,现在分享给大家,也给大家做个参考。一起跟随小编过来看看吧
Spring Security基于xml配置
引入坐标 web.xml配置 配置spring secruity 过滤器 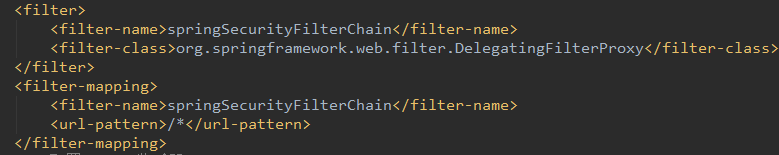 配置Spring Listenter 配置SpringMVC 前端控制器 配置spring-security.xml ...
Spring Security 登陆成功后的处理
Spring Security 完成登陆后一般需要一些自定义的处理,例如,记录登陆日志,初始化用户菜单等等 这里就需要自定义的 登陆成功处理了,Spring 提供了 AuthenticationSuccessHandler 接口,完成这个接口就可以了。 但是,修改到这里处理后,原先系统的自动转向处理就没有了,接口中应该怎么写,才可以保持原来的功能呢? 代码如下: ...
Spring boot + Spring Security 简单配置实例
Spring boot + Spring Security 简单配置,数据库采用MongoDB
spring-security多登录页面配置
spring-security多登录页面配置,包括前台和后台分开登录界面,注销登录返回不同的界面等。




