

 交换及路由技术

关于双NAT请帮我看下这个实验
 墨衍会员 · AI 创作全网分发 墨衍智能分发 通过墨衍一键同步至各平台 可同步平台 CSDN微信公众号微博知乎掘金百家号博客园抖音小红书 你的文章也可以这样分发 墨衍会员 ¥399起/年,写一次发全网
我也要 关注 + 加入社区
做了半天实在不通,请各位帮看看是哪里有问题:
基本拓扑如图:
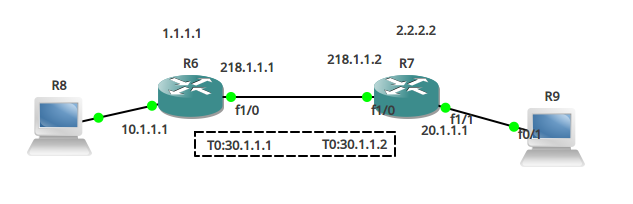
请无视那个T0
R6、R7(C7200)为两个NAT服务器,算公网接入吧,R8、R9本来该是主机暂用路由代替(C2600),路由上配置了Rip,NAT,Loopback(测试用),以R8为例,测试结果如图:
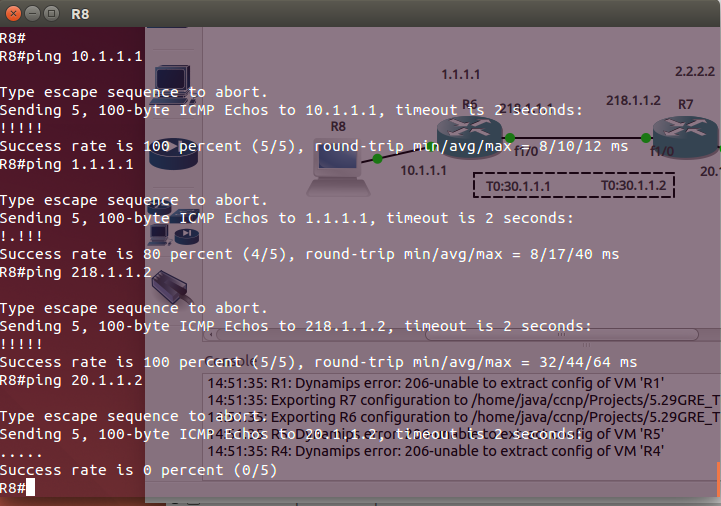
即R8--R6通,R8-R6 loopback通,R8-R9通,但就是R8到R9的inside不通了,抓包数据请看下图:
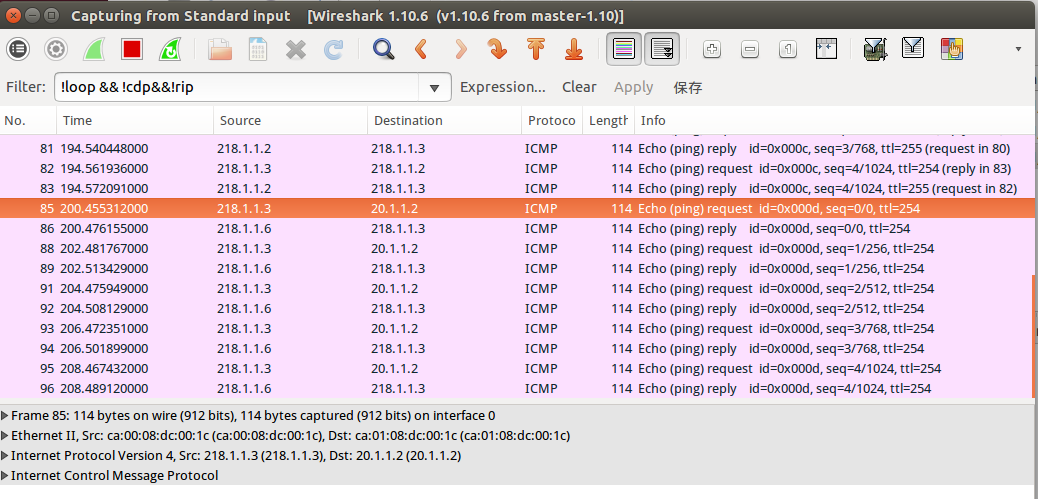
这是从R7的F1/1口上抓的,应该是从85号开始。
各设备start conf如下:
R6:
!
!
upgrade fpd auto
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R6
!
boot-start-marker
boot-end-marker
!
logging message-counter syslog
!
no aaa new-model
ip source-route
no ip icmp rate-limit unreachable
ip cef
!
!
!
!
no ip domain lookup
no ipv6 cef
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
memory-size iomem 0
archive
log config
hidekeys
!
!
!
!
!
ip tcp synwait-time 5
!
!
!
!
interface Loopback0
ip address 1.1.1.1 255.255.255.0
!
interface FastEthernet0/0
no ip address
shutdown
duplex half
!
interface FastEthernet1/0
ip address 218.1.1.1 255.255.255.0
ip nat outside
ip virtual-reassembly
duplex auto
speed auto
!
interface FastEthernet1/1
ip address 10.1.1.1 255.255.255.0
ip nat inside
ip virtual-reassembly
duplex auto
speed auto
!
router rip
version 2
network 1.0.0.0
network 10.0.0.0
network 218.1.1.0
no auto-summary
!
ip forward-protocol nd
no ip http server
no ip http secure-server
!
!
ip nat pool NAT 218.1.1.3 218.1.1.4 netmask 255.255.255.0
ip nat inside source list 1 pool NAT overload
!
access-list 1 permit 10.1.1.0 0.0.0.255
!
!
!
!
!
!
control-plane
!
!
!
mgcp fax t38 ecm
!
!
!
!
gatekeeper
shutdown
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line vty 0 4
login
!
end
R7:
!
!
upgrade fpd auto
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R7
!
boot-start-marker
boot-end-marker
!
logging message-counter syslog
!
no aaa new-model
ip source-route
no ip icmp rate-limit unreachable
ip cef
!
!
!
!
no ip domain lookup
no ipv6 cef
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
memory-size iomem 0
archive
log config
hidekeys
!
!
!
!
!
ip tcp synwait-time 5
!
!
!
!
interface Loopback0
ip address 2.2.2.2 255.255.255.0
!
interface FastEthernet0/0
no ip address
shutdown
duplex half
!
interface FastEthernet1/0
ip address 218.1.1.2 255.255.255.0
ip nat outside
ip virtual-reassembly
duplex auto
speed auto
!
interface FastEthernet1/1
ip address 20.1.1.1 255.255.255.0
ip nat inside
ip virtual-reassembly
duplex auto
speed auto
!
router rip
version 2
network 2.0.0.0
network 20.0.0.0
network 218.1.1.0
no auto-summary
!
ip forward-protocol nd
no ip http server
no ip http secure-server
!
!
ip nat pool NAT 218.1.1.5 218.1.1.6 netmask 255.255.255.0
ip nat inside source list 1 pool NAT overload
!
access-list 1 permit 20.1.1.0 0.0.0.255
!
!
!
!
!
!
control-plane
!
!
!
mgcp fax t38 ecm
!
!
!
!
gatekeeper
shutdown
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line vty 0 4
login
!
end
R8:
!
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R8
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
no ip routing
no ip icmp rate-limit unreachable
no ip cef
ip tcp synwait-time 5
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
interface FastEthernet0/0
no ip address
no ip route-cache
shutdown
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 10.1.1.2 255.255.255.0
no ip route-cache
duplex auto
speed auto
!
ip default-gateway 10.1.1.1
!
!
no ip http server
no ip http secure-server
!
!
!
!
!
!
control-plane
!
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
line vty 0 4
login
!
!
end
R9:
!
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R9
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
no ip routing
no ip icmp rate-limit unreachable
no ip cef
ip tcp synwait-time 5
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
interface FastEthernet0/0
no ip address
no ip route-cache
shutdown
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 20.1.1.2 255.255.255.0
no ip route-cache
duplex auto
speed auto
!
ip default-gateway 20.1.1.1
!
!
no ip http server
no ip http secure-server
!
!
!
!
!
!
control-plane
!
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
line vty 0 4
login
!
!
end
求教,可追分
基本拓扑如图:
请无视那个T0
R6、R7(C7200)为两个NAT服务器,算公网接入吧,R8、R9本来该是主机暂用路由代替(C2600),路由上配置了Rip,NAT,Loopback(测试用),以R8为例,测试结果如图:
即R8--R6通,R8-R6 loopback通,R8-R9通,但就是R8到R9的inside不通了,抓包数据请看下图:
这是从R7的F1/1口上抓的,应该是从85号开始。
各设备start conf如下:
R6:
!
!
upgrade fpd auto
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R6
!
boot-start-marker
boot-end-marker
!
logging message-counter syslog
!
no aaa new-model
ip source-route
no ip icmp rate-limit unreachable
ip cef
!
!
!
!
no ip domain lookup
no ipv6 cef
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
memory-size iomem 0
archive
log config
hidekeys
!
!
!
!
!
ip tcp synwait-time 5
!
!
!
!
interface Loopback0
ip address 1.1.1.1 255.255.255.0
!
interface FastEthernet0/0
no ip address
shutdown
duplex half
!
interface FastEthernet1/0
ip address 218.1.1.1 255.255.255.0
ip nat outside
ip virtual-reassembly
duplex auto
speed auto
!
interface FastEthernet1/1
ip address 10.1.1.1 255.255.255.0
ip nat inside
ip virtual-reassembly
duplex auto
speed auto
!
router rip
version 2
network 1.0.0.0
network 10.0.0.0
network 218.1.1.0
no auto-summary
!
ip forward-protocol nd
no ip http server
no ip http secure-server
!
!
ip nat pool NAT 218.1.1.3 218.1.1.4 netmask 255.255.255.0
ip nat inside source list 1 pool NAT overload
!
access-list 1 permit 10.1.1.0 0.0.0.255
!
!
!
!
!
!
control-plane
!
!
!
mgcp fax t38 ecm
!
!
!
!
gatekeeper
shutdown
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line vty 0 4
login
!
end
R7:
!
!
upgrade fpd auto
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R7
!
boot-start-marker
boot-end-marker
!
logging message-counter syslog
!
no aaa new-model
ip source-route
no ip icmp rate-limit unreachable
ip cef
!
!
!
!
no ip domain lookup
no ipv6 cef
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
memory-size iomem 0
archive
log config
hidekeys
!
!
!
!
!
ip tcp synwait-time 5
!
!
!
!
interface Loopback0
ip address 2.2.2.2 255.255.255.0
!
interface FastEthernet0/0
no ip address
shutdown
duplex half
!
interface FastEthernet1/0
ip address 218.1.1.2 255.255.255.0
ip nat outside
ip virtual-reassembly
duplex auto
speed auto
!
interface FastEthernet1/1
ip address 20.1.1.1 255.255.255.0
ip nat inside
ip virtual-reassembly
duplex auto
speed auto
!
router rip
version 2
network 2.0.0.0
network 20.0.0.0
network 218.1.1.0
no auto-summary
!
ip forward-protocol nd
no ip http server
no ip http secure-server
!
!
ip nat pool NAT 218.1.1.5 218.1.1.6 netmask 255.255.255.0
ip nat inside source list 1 pool NAT overload
!
access-list 1 permit 20.1.1.0 0.0.0.255
!
!
!
!
!
!
control-plane
!
!
!
mgcp fax t38 ecm
!
!
!
!
gatekeeper
shutdown
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
stopbits 1
line vty 0 4
login
!
end
R8:
!
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R8
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
no ip routing
no ip icmp rate-limit unreachable
no ip cef
ip tcp synwait-time 5
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
interface FastEthernet0/0
no ip address
no ip route-cache
shutdown
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 10.1.1.2 255.255.255.0
no ip route-cache
duplex auto
speed auto
!
ip default-gateway 10.1.1.1
!
!
no ip http server
no ip http secure-server
!
!
!
!
!
!
control-plane
!
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
line vty 0 4
login
!
!
end
R9:
!
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R9
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
no ip routing
no ip icmp rate-limit unreachable
no ip cef
ip tcp synwait-time 5
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
interface FastEthernet0/0
no ip address
no ip route-cache
shutdown
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 20.1.1.2 255.255.255.0
no ip route-cache
duplex auto
speed auto
!
ip default-gateway 20.1.1.1
!
!
no ip http server
no ip http secure-server
!
!
!
!
!
!
control-plane
!
!
!
line con 0
exec-timeout 0 0
privilege level 15
logging synchronous
line aux 0
exec-timeout 0 0
privilege level 15
logging synchronous
line vty 0 4
login
!
!
end
求教,可追分
...全文
相关推荐
路由器静态NAT配置实验
这是一份关于路由器静态NAT配置的实验报告-------实验。
ensp实验-NAT实验
1、1、静态NAT:静态NAT是指内部本地地址一对一转换成内部全局地址,一般用于在内网中对外提供服务的服务器。2、,允许多个设备共享一个公网IP地址进行互联网通信。网络地址转换(NAT)技术在现代网络通信中扮演着至关重要的角色,尤其是在IPv4地址日益紧缺的情况下。动态NAT之NAPT正是这一技术的重要组成部分。通过这种技术手段,内部网络中的设备能够以共享的方式使用单个公网IP地址进行通信,极大地提高了IP地址资源的利用率。
ACL+NAT综合实验
在Router 上作NAT并且做一条默认路由指向File Server的IP,要求在Router 上能查看到NAT映射的效果,并且能实现PC 1通过NAT ping 通File Server……
静态nat 实验报告
静态nat实验报告,使用静态方法实现nat
NAT实验报告
我想通过我的实验帮助更多人走向网络,了解资源,资源分享。




